Find vulnerabilities before attackers do.
Continuously discover, test, prioritize, and remediate security risk across your entire environment — from one platform.
Organization security score
Live
Computed from your findings
Critical vulnerabilities
Live
From completed assessments
Overdue remediation
Live
SLA-tracked tickets
Compliance coverage
Live
Mapped control status
Every number in Guardian comes from a database query against your own scan data. No sample dashboards, no synthetic findings.
The lifecycle
Discover. Test. Prioritize. Remediate. Verify. Prove.
Guardian runs the full vulnerability lifecycle instead of stopping at a scan report.
Discover
Automatically discover infrastructure, applications, cloud resources, SaaS platforms and exposed services.
Test
Continuously test networks, servers, endpoints, cloud, web apps, APIs, source code, containers and SaaS environments.
Prioritize
Turn thousands of vulnerabilities into a roadmap based on exploitability, exposure, business importance and compliance impact.
Remediate
Route findings to the responsible teams through Guardian Tickets, Jira or ServiceNow with owners and due dates.
Verify
Automatically retest vulnerabilities to confirm the fix actually worked — and reopen the ticket when it did not.
Prove
Generate technical control coverage and executive reporting for HIPAA, PCI DSS, FedRAMP, NIST, CMMC, SOC 2 and ISO 27001.
In practice
Security teams, engineers and executives working from the same truth
Guardian gives every team the view they need — the SOC triaging live findings, engineers fixing them, and the board seeing risk fall.
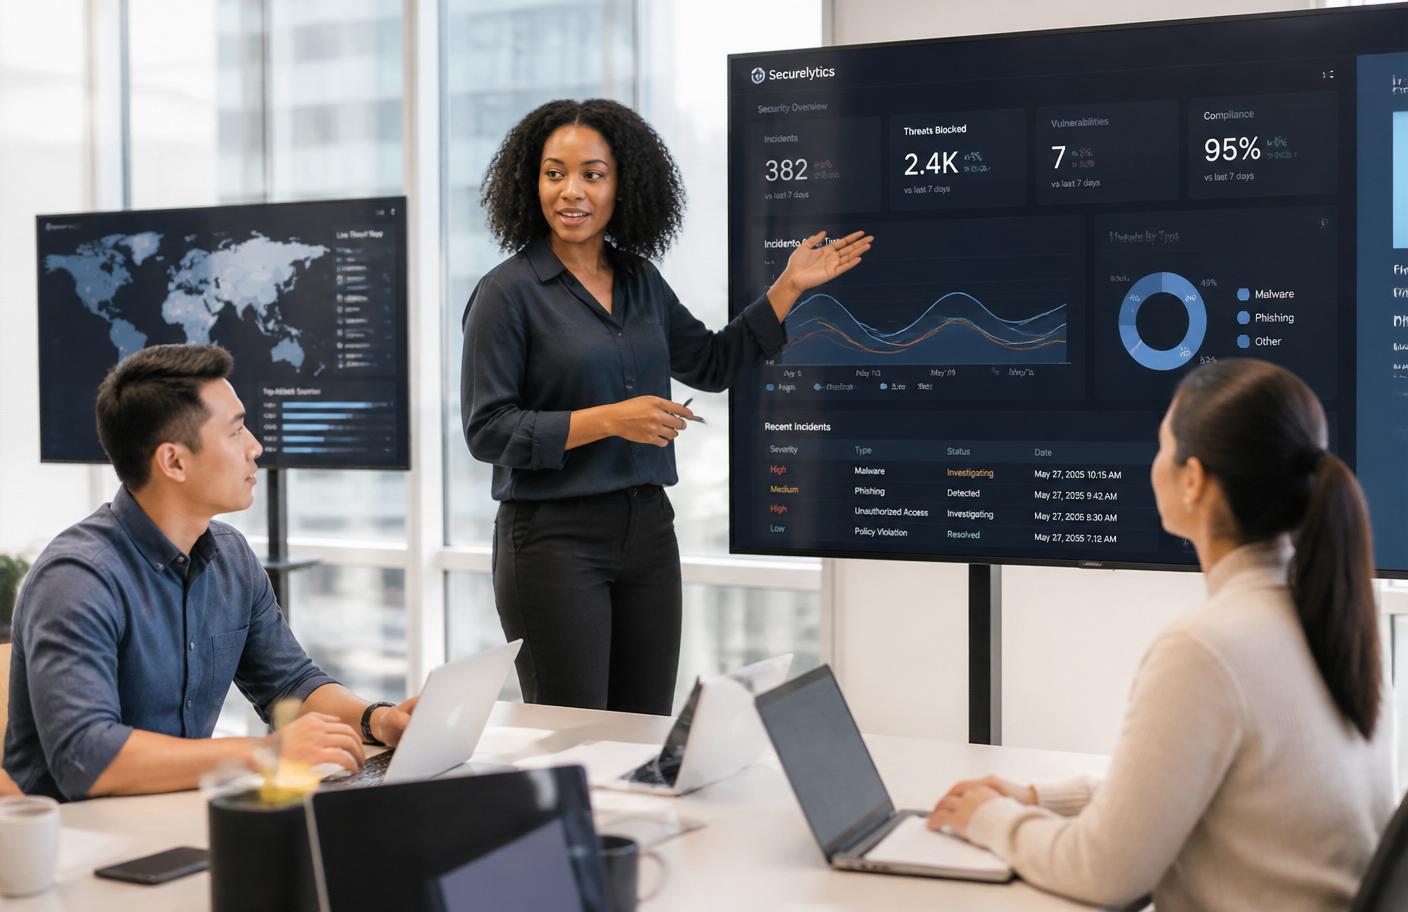
Analysts stop drowning in scan output
Findings arrive normalized, de-duplicated and scored, so the team works the twelve issues that matter instead of twelve hundred rows.
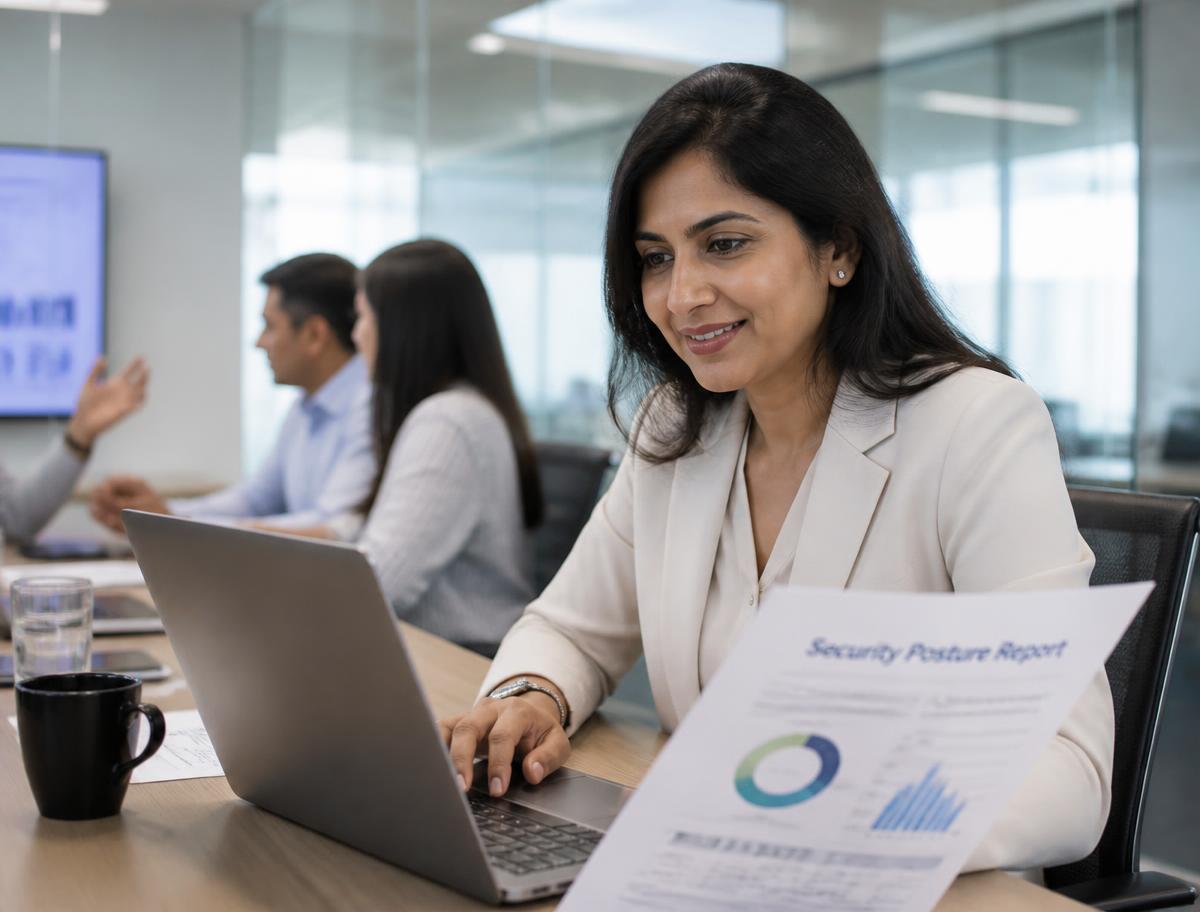
Owners know what is theirs to fix
Every asset has an owner, a criticality and a remediation queue with due dates — so accountability does not live in a spreadsheet.
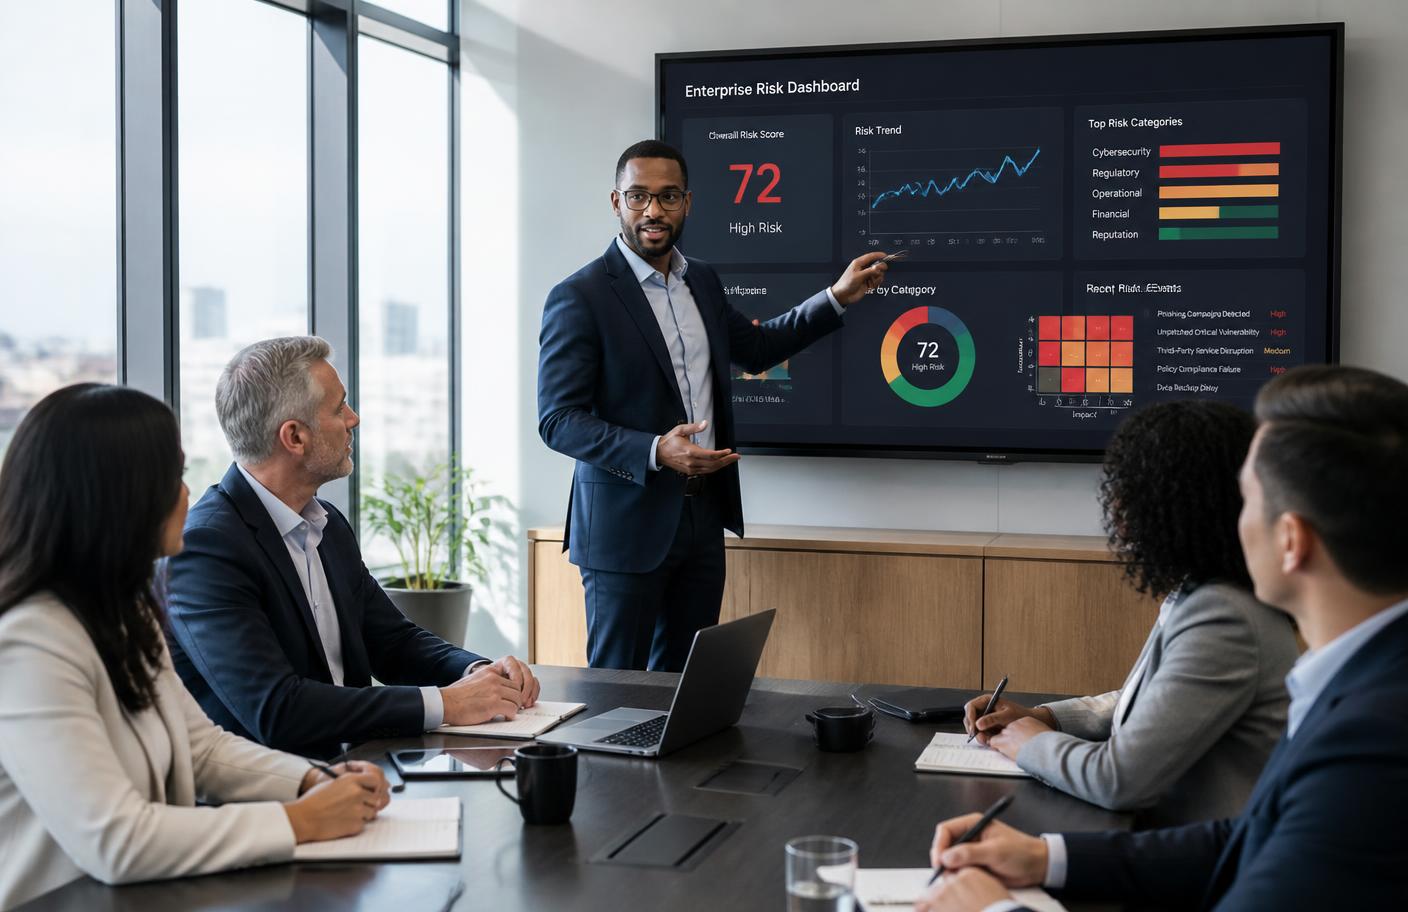
Leadership gets an answer, not a scan file
Executive and CISO reports translate technical findings into risk trend, exposure and framework coverage your board can act on.
Coverage
One platform across every attack surface
Network, endpoint, application, API, container, cloud and SaaS testing feed a single normalized findings model.
External attack surface
- Domains and subdomains
- Public IPs and open ports
- Certificates and TLS
- Exposed technologies
Internal network
- Agent-based discovery
- Service enumeration
- Configuration assessment
- Patch status
Applications and code
- SAST on your repositories
- DAST against running apps
- API security testing
- Dependency and secret scanning
Cloud and SaaS
- AWS, Azure and GCP posture
- Microsoft 365 and Entra ID
- Salesforce security
- Container and Kubernetes
Our own posture
Built to the standards we help you meet
Guardian's internal controls are designed and operated in alignment with the frameworks our customers are measured against. We hold ourselves to the same evidence we ask of your environment.
Aligned with
SOC 2 Type II
Security, availability & confidentiality criteria
Change management, access reviews and monitoring run continuously against the Trust Services Criteria.
Aligned with
HITRUST CSF
Healthcare-grade control depth
Data handling, encryption and incident response follow HITRUST CSF control expectations for regulated data.
Aligned with
ISO/IEC 27001
Information security management system
Risk register, asset ownership and supplier review mirror the Annex A control set.
Encrypted end to end
TLS 1.2+ in transit, AES-256 at rest, per-tenant key scoping.
Least privilege by default
Row-level isolation per organization, nine graded roles, TOTP MFA.
Immutable audit trail
Every mutation, scan and agent check-in is recorded and exportable.
Hardened, isolated runtime
No shared tenant state; scan engines execute in a sandboxed worker runtime.
Secrets never leave the vault
Integration credentials are write-only and never rendered back to the browser.
We scan ourselves
Guardian runs its own SAST, DAST and dependency assessments on every release.
Alignment statement: Guardian designs and operates its controls in accordance with the principles of SOC 2 Type II, HITRUST CSF and ISO/IEC 27001. These are statements of control alignment, not certifications or third-party attestations. Our current control documentation and security questionnaire responses are available on request.
Answers
The questions your security program has to answer
Guardian is built so each of these has a query behind it, not a slide.
Start your first security assessment
Create your organization, add your first assets and authorize a target. Guardian handles discovery, testing, prioritization and remediation tracking from there.